
INDUSTRIAL SMEs / PRACTICAL GUIDE
Keep the process
in view.
A starting point for industrial cyber security.
When equipment and software support a physical process, a security decision can affect production, reliability, and safety. Use the ISA guide to bring operations and technology into the same conversation.
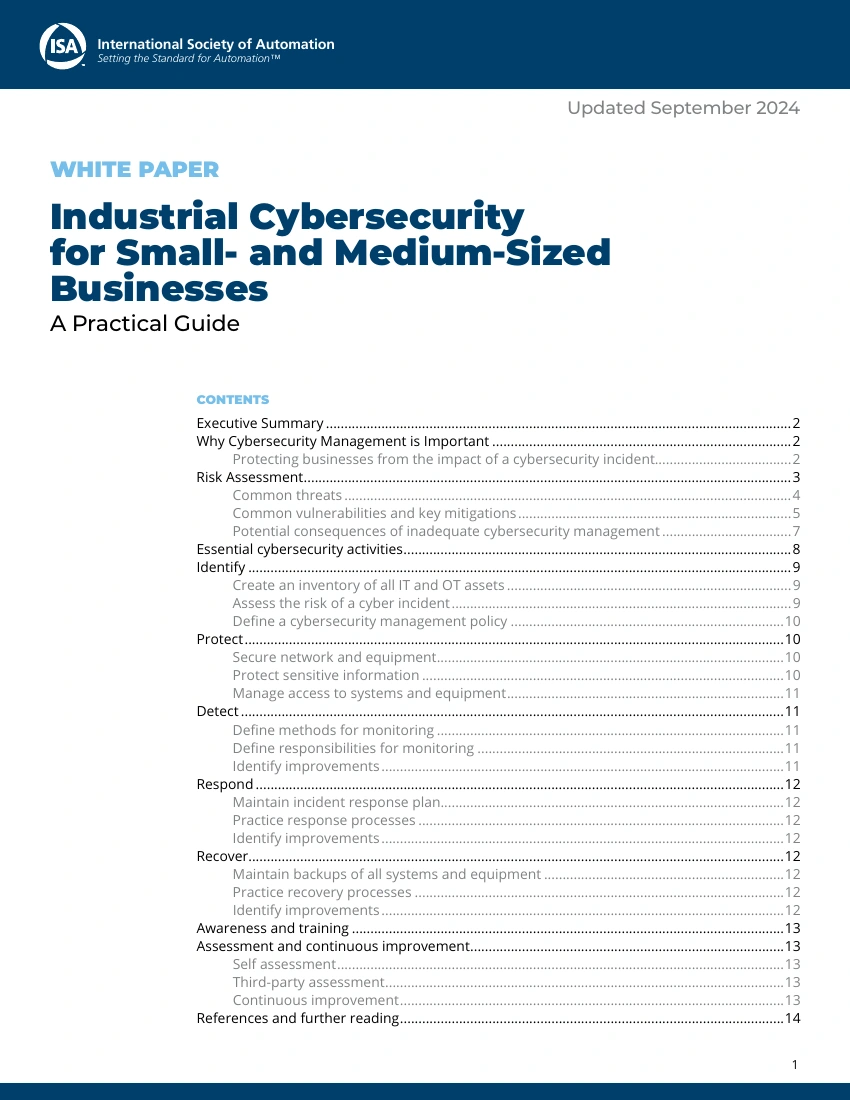
Start with the consequence of disruption.
Choose a process the business depends on. Ask what would happen if its controls became unavailable, its configuration changed unexpectedly, or its operators could no longer trust the information they see.
ISA’s guide covers risk assessment, essential protective activities, monitoring, response, recovery, and improvement for smaller industrial businesses. Read its recommendations in the context of your actual equipment and operating constraints.
OPERATIONS
What must
keep working?
Process knowledge, safe operating conditions, maintenance constraints, and recovery priorities.
TECHNOLOGY
What could
affect it?
Connected systems, access paths, supplier support, configuration changes, and recovery dependencies.
AN OPERATIONAL REVIEW
Work from a process
to a small set of decisions.
UNDERSTAND
Identify the systems and the owner.
Bring the process owner together with engineering and IT. Record the equipment, software, and external support the process depends on, including less obvious maintenance connections.
CONTROL
Examine access and changes.
Ask who can connect or make a change, how approval works, and what evidence is kept. Include temporary access and work carried out by suppliers.
RECOVER
Test what restoration requires.
Check that the team can obtain the right configurations, specialist support, and instructions. Plan a controlled test appropriate to the process and its safety constraints.
CHANGE SAFELY
A desktop fix is not automatically
a safe plant change.
Do not scan, patch, disconnect, or test live operational equipment solely because a general guide suggests a control. Involve the responsible engineering and safety personnel, assess the consequences, and use the site’s approved change arrangements.
USE THE GUIDE IN CONTEXT
Build the programme around your site.
Assign someone to coordinate the work and maintain a realistic improvement plan. Give operators a clear route for reporting unexpected behaviour, and decide who will assess those reports.
The ISA/IEC 62443 series provides a wider industrial-security reference. The NIST Cybersecurity Framework is another management resource. A short white paper does not replace a site-specific risk assessment, a safety case, or specialist engineering judgement.
YOUR NEXT REVIEW
Bring one recovery assumption
to the team.
Identify what the business currently assumes it can restore. Ask for the evidence, identify any missing dependency, and agree the next safe test.
Make the next improvement specific.
CyberSolace can help you organise the risk discussion and define proportionate next steps with your operational team.
SOURCES & REVIEW
ISA industrial SME white paper · ISA/IEC 62443 information · NIST Cybersecurity Framework. The linked ISA edition is dated September 2024. Review prompts are CyberSolace suggestions.
Originally published 30 July 2017. Resource links and presentation reviewed 20 October 2026.